🤖 7-day agentic security challenge, self-paced by email
Find and fix the riskiest AI agents in your company in 7 days
One task a day, each under 30 minutes, delivered to your inbox. By day 7 you have a full agent inventory, a risk score for each agent and a one-page security policy you can adopt.
Your team shipped AI agents. Nobody threat-modelled them.
A support copilot reads customer emails. A coding assistant can push to your repos. Someone wired an LLM into a workflow that sends invoices.
Each one acts with real credentials, reads content outsiders can write, and decides its own next step. Your existing controls were built for users and services, not for software that can be talked into things.
- You can't say how many agents are running, or who owns them
- Agents use one shared API key with access to everything
- Third-party MCP servers were connected without review
- Your auditors or customers have started asking how you govern AI
Seven daily tasks, each one builds a single inventory
Every email explains one idea and gives you one task to complete that day. Each task adds columns to the same spreadsheet, so by day 7 you hold a working risk register for every agent you run.
Days 1-2: map and score
Inventory every agent, then score each one against the three conditions that turn prompt injection into a data breach.
Days 3-4: tools and identity
Sort agent tools into three risk tiers, decide where humans approve, and replace shared service accounts with scoped identities.
Days 5-7: supply chain to policy
Review MCP servers for tool poisoning, lock down agent memory and RAG, then turn it all into a one-page policy.
What you'll have at the end of the week
- A complete inventory of every AI agent, its owner and its tools
- A shortlist of agents exposed to data exfiltration through prompt injection
- Clear rules for which agent actions need human approval
- A review checklist for third-party MCP servers and plugins
- A one-page agent security policy mapped to OWASP and ISO/IEC 42001
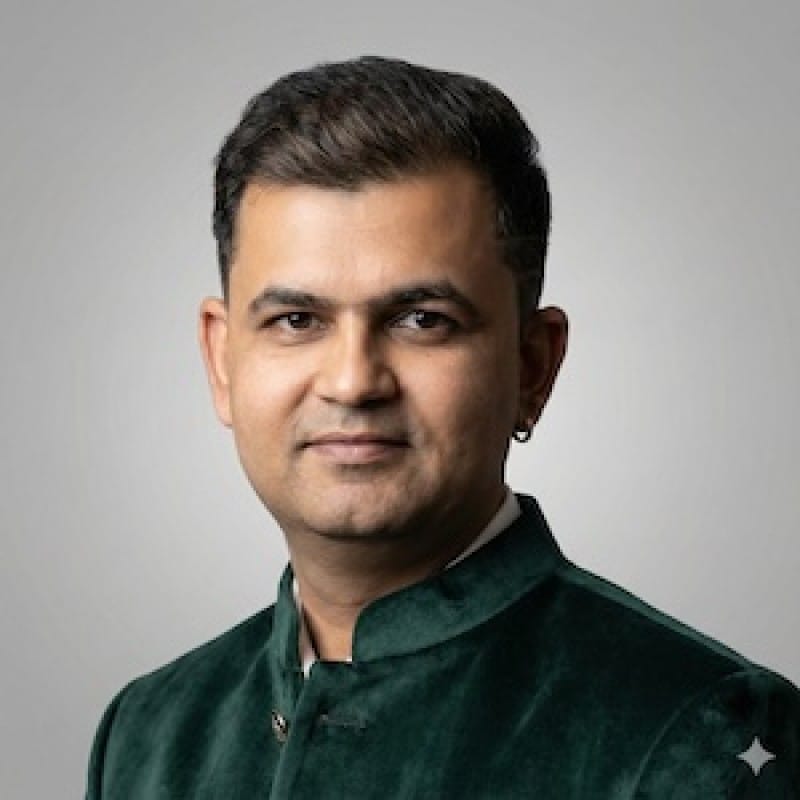
Written by someone who breaks these systems for a living
I'm Rohit Kaundal, founder of AIFortess in Dubai. I've spent more than ten years in offensive security: penetration testing, red teaming and cloud security across AWS, GCP and Azure.
I'm an ISO 42001 Lead Implementer and work on AI governance and agent security with companies deploying AI in production. This challenge is the baseline I walk clients through first, broken into seven daily tasks.
7
Tasks, one per day
<30 min
Per daily task
10+
Years of offensive security behind it
Questions before you start
No. The challenge suits CTOs, engineering leads, security and compliance owners. Technical terms are explained as they come up.
About 10 minutes to read each email and under 30 minutes for the task. It's self-paced, so if you miss a day, just pick up where you left off.
Yes. Vendor copilots, browser agents and AI features in SaaS tools are agents too, and they go into the same inventory.
Reply to any challenge email with your question and I'll answer personally.
The 7-day agentic security challenge
$27, one-time payment
- Seven daily tasks delivered by email
- Each task under 30 minutes, self-paced
- Tool risk tiers and MCP server review checklist
- One-page agent security policy you can adopt
- Personal replies to your questions
You won't be left with unanswered questions
If a task doesn't fit your setup, reply to that day's email and describe what you're running. I'll answer personally so the task works for your agents.
Know exactly which AI agents put you at risk, by next week
Seven days, seven tasks, one policy. Start today.
© AIFortess Infosec FZCO, Dubai, UAE · hello@aifortess.com