OWASP-ALIGNED · ISO 42001 · CSA AI TRUSTWORTHY PLEDGE
Find out how your AI agent could be turned against you, before someone else does
A fixed-price expert review of one AI agent or LLM feature: its tools, permissions, credentials, data access and prompt injection exposure. You get a written report with every finding rated by severity and a prioritised fix list within 5 business days of the kickoff call.
01 — THE RISKYour agent passed QA. That doesn't mean it's safe.
Functional testing checks that the agent does what it should. Nobody checked what it can be talked into doing. An agent that reads outside content, holds real credentials and can call tools is a new kind of attack surface, and most teams ship it without a security review.
- A customer or prospect sent a security questionnaire asking how you secure your AI features
- Your agent can send email, write to a database or call internal APIs
- It reads content outsiders can write: tickets, emails, web pages, uploads
- You've connected third-party MCP servers or plugins nobody reviewed
02 — SCOPEWhat the review covers
One AI agent or LLM-powered feature, reviewed against the risks that actually lead to incidents.
Prompt injection exposure
Where untrusted content reaches the model, and whether private data plus an outbound channel turn an injection into a breach.
Tools and permissions
Every tool the agent can call, its risk tier, and where a human approval step is missing.
Identity and credentials
Shared service accounts, long-lived keys, secrets in context, and gaps in your audit trail.
Tool supply chain
Third-party MCP servers and plugins, checked for tool poisoning risk, version pinning and scoped access.
Memory and RAG
Whether retrieval enforces permissions, whether memory can be poisoned, and how agent output is handled downstream.
Monitoring and controls
Logging of tool calls, alerting, kill switches, and mapping to the OWASP Top 10 for LLM applications.
03 — PROCESSHow it works
- Buy the review and book a 60-minute kickoff call at a time that suits you
- On the call, walk me through the agent: what it does, its tools, data and access
- Share architecture docs, configs or read-only access so I can review the setup
- Receive your written report within 5 business days of the kickoff call
You receive: a written report with every finding rated by severity, the evidence behind it, and a prioritised list of fixes your engineers can act on.
04 — REVIEWERWho does the review
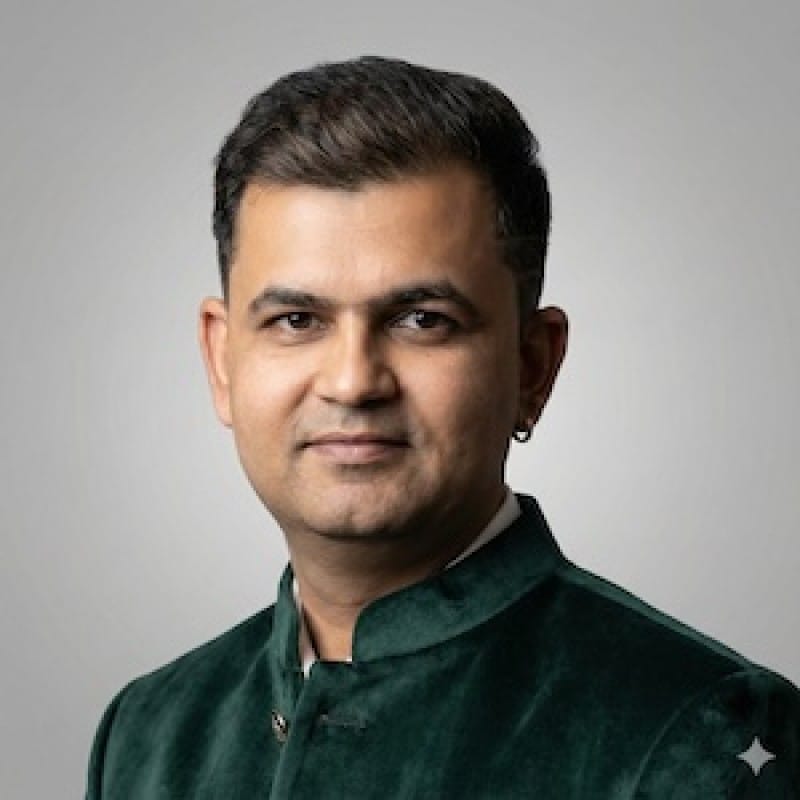
I'm Rohit Kaundal, founder of AIFortess in Dubai. I've spent more than ten years in offensive security: penetration testing, red teaming and cloud security across AWS, GCP and Azure.
I'm an ISO 42001 Lead Implementer and work on AI governance and agent security with companies deploying AI in production. AIFortess is founder-led: the person who reviews your agent is the person who writes your report, not a junior consultant.
10+
YEARS IN OFFENSIVE SECURITY
5 days
KICKOFF TO WRITTEN REPORT
$497
FIXED PRICE, NO SURPRISES
05 — QUESTIONSQuestions before you book
No. It's an expert review of your agent's design and configuration. I don't run live attacks against your production systems. If the review shows you need hands-on testing, I can scope that separately.
One AI agent, copilot or LLM-powered feature with its own tools and data access. If you have several, book one review per agent, or email hello@aifortess.com for a combined quote.
An hour for the kickoff call with someone who knows the agent's setup, plus architecture docs, configuration or read-only access shared after the call.
The report tells your team exactly what to fix and in what order. If you'd like help implementing the fixes, that can be quoted separately.
06 — PRICINGAI agent security review
$497 FIXED PRICE · ONE AGENT
- 60-minute kickoff call
- Review of one AI agent or LLM feature
- Written report with severity-rated findings
- Prioritised fix list for your engineers
- Report within 5 business days of the kickoff
07 — DELIVERABLEA report your engineers can act on
Every finding comes with the evidence behind it and a concrete fix, ordered by severity. If anything in the report is unclear, reply and I'll walk your team through it.
Know where your agent is exposed, next week
One call, one report, a clear list of fixes.